November 17, 2026
Backup Restore Testing: A Practical Checklist for Malaysian SMEs
Bahasa Melayu — artikel penuh
Ujian pemulihan sandaran untuk PKS Malaysia
Sandaran yang dilaporkan berjaya belum membuktikan perniagaan boleh memulihkan fail dan sistem apabila diperlukan. Ujian pemulihan terkawal membantu PKS Malaysia mengetahui data yang tersedia, masa pemulihan dan tindakan yang perlu dibaiki. Ia melengkapi pelan kesinambungan perniagaan dan tidak menjamin pemulihan daripada setiap insiden.
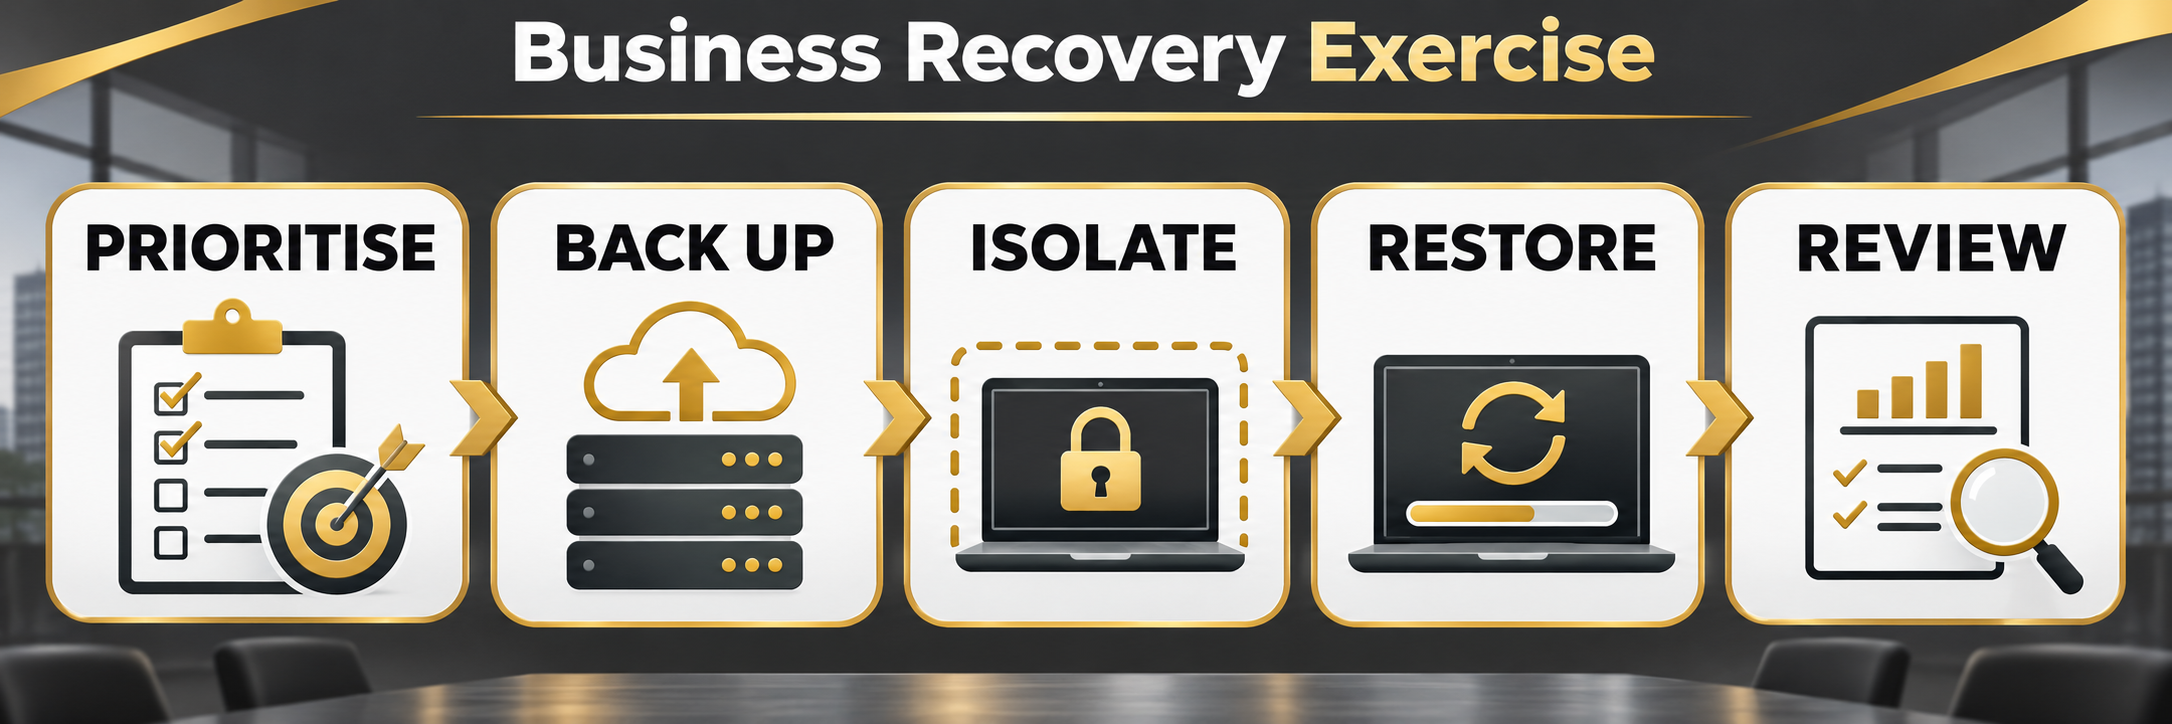
1. Pilih perkhidmatan yang penting
Senaraikan sistem yang menyokong invois, fail pelanggan, lukisan, e-mel atau operasi tapak. Tetapkan pemilik perniagaan dan kesan jika perkhidmatan terhenti. Pilih satu sistem atau set fail untuk ujian pertama. Tetapkan sasaran masa pemulihan dan kehilangan data yang boleh diterima berdasarkan keperluan sebenar, bukan janji pembekal semata-mata.
2. Kenal pasti salinan dan akses
Rekod lokasi sandaran, kekerapan, tempoh simpanan, kaedah penyulitan dan orang yang boleh mengaksesnya. CISA mengesyorkan salinan luar talian dan ujian pemulihan berkala untuk mengurangkan kesan ransomware. Salinan di luar talian perlu dikendalikan mengikut prosedur organisasi. Semak bahawa bukti kelayakan dan kunci pemulihan boleh dicapai oleh orang yang diberi kuasa ketika sistem utama tidak tersedia.
3. Rancang ujian selamat
Gunakan persekitaran ujian berasingan dan data yang sesuai. Jangan memulihkan sandaran ujian di atas sistem produksi. Tentukan masa ujian, pemilik, langkah, hasil dijangka dan cara menghentikan ujian jika terdapat risiko. Jika data peribadi terlibat, hadkan akses dan tempoh penyimpanan salinan ujian.
4. Pulihkan dan sahkan
Pilih titik pemulihan yang ditetapkan, pulihkan fail atau sistem dan ukur masa sebenar. Buka sampel fail bersama pemilik perniagaan. Bagi aplikasi, semak kebergantungan seperti pangkalan data, konfigurasi, lesen dan sambungan. Kejayaan teknikal tidak mencukupi jika pengguna tidak boleh menjalankan proses penting.
5. Catat keputusan dan jurang
Rekod masa mula dan tamat, umur data, fail yang gagal, kebergantungan hilang dan keputusan pengguna. Bandingkan dengan sasaran yang dipersetujui. Lantik pemilik bagi setiap tindakan pembetulan dan uji semula. Jangan anggap salinan hilang sebagai data kosong atau menyembunyikan kegagalan.
6. Jadikan ujian rutin
Jadualkan semakan berkala berdasarkan kepentingan sistem dan perubahan perniagaan. Selang-selikan ujian fail, aplikasi dan pemulihan yang lebih luas apabila sesuai. Kemas kini prosedur apabila kakitangan, pembekal atau sistem berubah. Simpan salinan pelan hubungan dan arahan di lokasi yang boleh diakses semasa gangguan.
Senarai semak pengurusan
- Perkhidmatan dan pemilik dikenal pasti.
- Sasaran masa dan kehilangan data dipersetujui.
- Salinan serta akses pemulihan disahkan.
- Pemulihan diuji dalam persekitaran berasingan.
- Pengguna mengesahkan hasil dan jurang diperbaiki.
Terokai perkhidmatan IT FXIT dan bincangkan keperluan. Sahkan skop sokongan dan tanggungjawab pembekal sebelum perolehan.
简体中文 — 完整文章
马来西亚中小企业备份恢复测试
备份任务显示成功,并不证明企业在需要时能恢复文件和系统。受控恢复测试帮助马来西亚中小企业了解可用数据、恢复耗时和需要改进的环节。它是业务连续性计划的一部分,不能保证应对所有事故。
1. 选择重要服务
列出支持开票、客户文件、图纸、电子邮件或现场运营的系统,明确业务负责人及停机影响。首次选择一个系统或一组文件。根据实际业务需求商定可接受的恢复时间和数据损失,而不是只依赖供应商承诺。
2. 确认备份副本和访问权
记录备份位置、频率、保留期、加密方法及可访问人员。CISA 建议保留离线备份并定期测试恢复,以降低勒索软件的影响。离线副本应按照企业程序管理。确认主系统不可用时,获授权人员仍可取得恢复凭据和密钥。
3. 安全规划测试
使用独立测试环境和合适的数据,不要把测试恢复覆盖到生产系统。确定时间、负责人、步骤、预期结果和出现风险时的停止方法。涉及个人数据时,应限制测试副本的访问和保留期限。
4. 恢复并验证
选择指定恢复点,恢复文件或系统并测量实际耗时。与业务负责人一起打开抽样文件。应用系统还应检查数据库、配置、许可和网络连接等依赖。若用户无法完成关键业务流程,仅有技术层面的成功并不足够。
5. 记录结果和差距
记录开始与结束时间、数据更新时间、恢复失败文件、缺失依赖和用户验收结果,并与商定目标比较。为每项整改指定负责人和期限,然后重新测试。不能把缺失副本当作空数据,也不应隐藏失败。
6. 形成定期流程
根据系统重要性和业务变化安排定期测试。适当交替测试单个文件、应用程序和更大范围恢复。人员、供应商或系统变化时更新程序。将联系清单和操作说明保存在故障期间仍可访问的位置。
管理层检查清单
- 确认关键服务和负责人。
- 商定恢复时间与可接受数据损失。
- 验证备份副本及恢复访问权。
- 在隔离测试环境中恢复。
- 由业务用户验收并整改差距。
查看 FXIT IT 服务 并 讨论需求。采购前应确认供应商的具体支持范围和责任。
Backup restore testing for Malaysian SMEs
Backup restore testing helps a Malaysian SME answer a question that a green dashboard cannot: can the business actually recover the files and systems it needs? A backup job may report success while a recovery is slowed by missing credentials, an unavailable application dependency or an untested procedure. A controlled exercise reveals those gaps before an emergency. It supports business continuity but cannot guarantee recovery from every incident.
1. Choose a critical service
List the systems that support invoicing, customer records, engineering drawings, email and site operations. Ask the business owner what happens if each service is unavailable and which data must be recovered first. Pick one system or a representative file set for the first exercise rather than attempting the whole business in a single afternoon.
Agree on a target recovery time and an acceptable amount of data loss based on operational needs. These are planning targets, not promises. Record assumptions such as staff availability and whether the cloud service, office network and backup storage are themselves accessible.
2. Locate copies and recovery access
Document where backups reside, how often they run, how long versions are retained, how they are encrypted and who can access them. Check that a recovery operator can reach the backup when the primary system is unavailable. CISA recommends maintaining offline backups and testing restoration regularly as part of ransomware resilience.
Keep recovery credentials and encryption keys protected and accessible only to authorised people. Test the access procedure without exposing secrets in the exercise report. Clarify who supplies the backup, who monitors failures and who is responsible for restoring the service if an external provider is involved.
3. Plan an isolated test
Use a separate test environment and a suitable sample of data. Do not restore test data over production systems. Define the test window, participants, steps, expected result and a stop condition if an unexpected risk appears. Where personal or confidential information is involved, limit access and decide how long the test copy will be kept.
Choose a recovery point deliberately. An apparently current backup may contain unwanted changes, while an older copy may miss important work. The test should establish whether the team can find and select the version it intends to restore.
4. Restore and validate with a user
Restore the selected files or system and measure elapsed time. Have a business owner open a sample of recovered documents and check that they are usable. For an application, inspect its database, configuration, licences and network dependencies. A server that starts successfully is not a complete recovery if users cannot carry out the critical workflow.
Document the time of the recovered data and compare it with the incident scenario. Keep the test separate from any real incident response. If the recovery fails, preserve the error and identify the failed step before changing several settings at once.
5. Record gaps and retest
Capture start and finish times, data age, missing files, unavailable dependencies and the user’s acceptance result. Compare the observed outcome with the agreed targets. Assign an owner and due date for each corrective action, then repeat the failed part of the test. Missing data should be reported as missing, not interpreted as an empty file or a successful zero.
For suppliers, ask for evidence of a restore test that covers the contracted service and clarify how the customer participates. A generic assurance that backups exist is not the same as evidence that the business can restore its own workflow.
6. Make testing routine
Set a recurring review based on system importance and business changes. Alternate file-level tests, application-level tests and broader exercises where appropriate. Update the procedure when people, providers, systems or retention policies change. Store contact details and recovery instructions where authorised staff can reach them during an outage.
Management checklist
- Critical service and business owner identified.
- Recovery time and data-loss targets agreed.
- Backup copies and recovery access verified.
- Restore performed in a separate test environment.
- Business user validates the result and gaps are assigned.
Explore FXIT IT services or discuss your requirements. Confirm the exact support scope and provider responsibilities before procurement.
Sources checked 17 November 2026: CISA: StopRansomware Guide; CISA: Protecting Your Networks from Ransomware.